Which AI is GDPR compliant? Using it in an Irish business
· Updated

Joaquín Trapero in AI and privacy expert, and founder of Nonimo.
People ask me for a list of the AI tools that are GDPR compliant, as though there were a stamp on the box. There isn’t one. In Ireland that is unusually easy to show, because the regulator watching most of these companies sits in Dublin and has said so in writing.
So this guide works from the Data Protection Commission’s record rather than from vendor pages: what it has done about each assistant, what it expects from a firm that uses one, and the paperwork that follows. If all you need is a list of what to strip from a document first, start there.
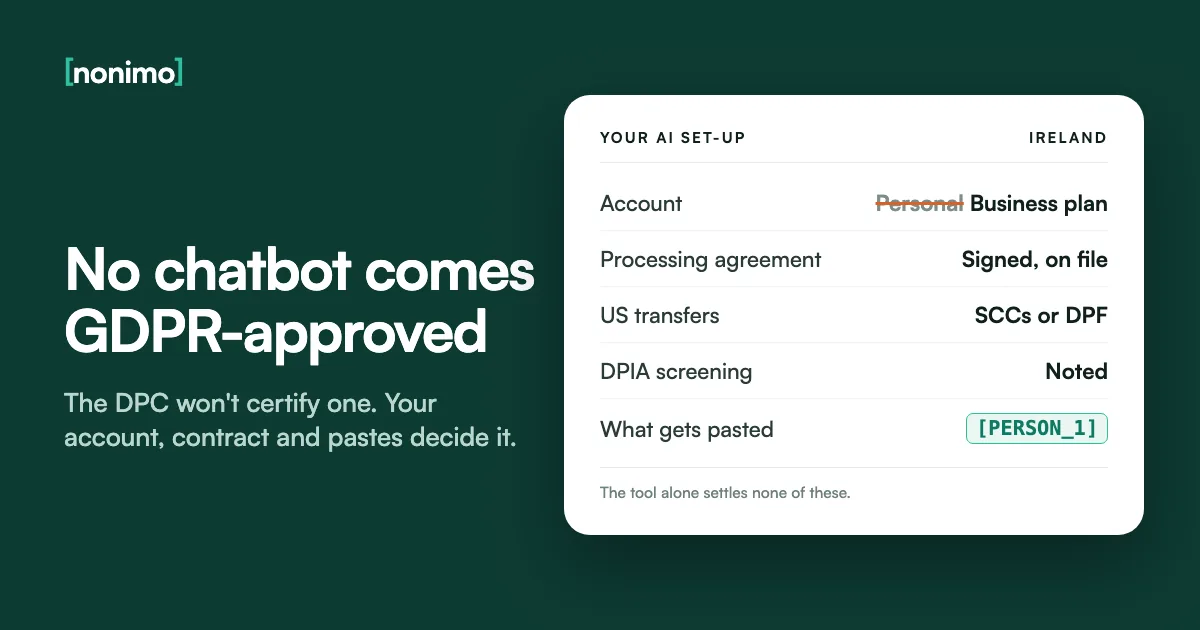
No AI tool is GDPR compliant on its own, and the DPC says it will never certify one. Whether your use is lawful turns on the account staff sign in with, the processing agreement behind it, where the data travels, whether you screened for a DPIA and what people actually paste.
Is any AI GDPR compliant? What the DPC says about approval
The GDPR regulates processing, not products. There is no register of approved assistants and no Irish certification scheme for them. The duties sit with the controller, and when staff use a chatbot for work, the controller is your firm, whatever the vendor’s website says about itself.
Vendors do use the word. Microsoft’s Copilot privacy page calls Copilot compliant with its existing GDPR commitments to commercial customers. That describes Microsoft’s half of a contract. It says nothing about the file someone in your office pasted on Tuesday, which is what a breach assessment would turn on.
Three times the DPC declined to call an AI use compliant
After securing five categories of change to LinkedIn's plan to train generative AI on members' data, the DPC said it had neither approved that use nor found it compliant.
Once Meta came back with a revised legitimate interests assessment and DPIA, the DPC saw no grounds for further injunctive action, and said in terms that it was not determining Meta had complied.
Its supervision work, the report says, "will never approve or state that a process, product, or service is compliant".
Sources: DPC statement on LinkedIn AI training, 7 November 2025; DPC, Responsible Artificial Intelligence Innovation (AI Insights Report), September 2026.
That third line is the most useful thing an Irish regulator has written on the subject. If the office that reads thousands of pages of these companies’ risk assessments won’t say “compliant”, I see no reason to accept the word from a sales deck.
ChatGPT, Copilot and the AI companies the DPC supervises
Most large providers run their European business through an Irish company, which makes the DPC their lead supervisory authority under the GDPR’s one-stop-shop. Its AI Insights Report names Google, Meta, Microsoft, OpenAI, LinkedIn, X and DeepSeek among the controllers it engaged with, and covers the period from 2021 to 2025.
In those five years its supervision unit dealt with about 180 AI products and services, 143 of them generative. In 2024 and 2025 combined, 59% of AI products launched in the EU left with recommendations from Dublin. For a firm using one, the AI policy template turns that into rules.
Generative AI engagements with the DPC's supervision unit
Each engagement is one product or feature the DPC examined, before or after launch.
Source: DPC AI Insights Report, September 2026, from internal supervision statistics. Bars are each year divided by 2025.
None of that is a verdict on your use, and transparency came up in 72% of the DPC’s AI recommendations. When a vendor says it has engaged with the regulator, my next question is which recommendations it got. Pick an assistant below for its Irish record.
The assistant your staff use, and its Irish record
OpenAI Ireland Limited, Dublin 1, is controller in the EEA under the Europe policy of 24 August 2026, with the DPC as lead authority; the September 2026 report listed no open DPC inquiry into ChatGPT. OpenAI signs a processing addendum for Business, Enterprise and the API, never a personal account: what OpenAI does with prompts.
Anthropic Ireland, Limited, Barrow Street, Dublin 4, is controller for Europe under the privacy policy of 10 September 2026. Anthropic is not among the companies the DPC report names, and the policy sends complaints to the authority where you live or work. Consumer chats train models unless you opt out: how Claude handles your data.
Google Ireland Limited provides Gemini Apps in the EEA and Switzerland. The DPC opened a section 110 inquiry on 12 September 2024 into whether Google owed a DPIA before training PaLM 2, still open when the report went to print. On 21 September 2026 it fined Google Ireland €403 million over location data, a separate matter: what Gemini keeps and who reads it.
Microsoft is on the DPC's list of supervised controllers. In a work tenant, prompts, responses and Microsoft Graph data don't train foundation models. Anthropic models inside Copilot sit outside the EU Data Boundary and stay off for EU tenants until an admin opts in: which Copilot you are actually in.
On 8 August 2024 the DPC went to the High Court under section 134 of the 2018 Act over Grok training. The case was struck out on 4 September 2024 on X's undertaking. Inquiries followed on 11 April 2025 (training) and 17 February 2026 (sexualised images, Articles 5, 6, 25 and 35).
In 2024 the DPC asked Meta to pause training on EU users' content before it started, and Meta did. It came back in February 2025 with a revised legitimate interests assessment and DPIA, took further recommendations, and the DPC decided against more injunctive action without finding compliance.
Sources: DPC AI Insights Report, September 2026, and DPC press releases; provider privacy documentation consulted 7 and 8 November 2026.
How to protect personal data from AI: the DPC’s list for users
The DPC’s guidance for organisations using AI products, published on 18 July 2024, is still the plainest thing it has written for deployers. Before you start, it says, understand what personal data the system uses and how, where it goes when a third party is involved, and whether it is kept or reused.
It then lists the risks a controller has to be ready for. Tick the ones your firm could answer today, in writing, for the assistant your staff really use rather than the one in the procurement file.
The DPC's risk list, as questions for your office
0 of 8 answered
Not ready for client data. Each blank is a question for the supplier or a line for your own policy.
Close. Write down the gaps: they are what a complaint to the DPC would ask about first.
All eight answered. Date the answers and put them in your record of processing.
Built from the risks in the DPC's guidance of 18 July 2024. Nothing you tick leaves your browser.
The second box is where I expect most small offices to stall. Once a client’s details sit in three people’s chat histories, finding and erasing them inside the month the GDPR allows is harder than it sounds, and ChatGPT’s delete buttons each leave something different behind.
GDPR, legal AI and Irish solicitors: free accounts against business plans
The Law Society of Ireland’s generative AI guidance names Copilot, ChatGPT, Claude and Gemini. It says free and paid consumer versions are not suitable for securely handling personal or client confidential data, and warns that solicitors should never assume an enterprise tool guarantees compliance either.
It also warns that privileged communications put into a GenAI model without safeguards may lose privilege. Section 47 of the Data Protection Act 2018 lets a solicitor’s practice process special category data for legal advice and proceedings. It says nothing about a provider receiving that data.
Can this account take client data?
Which account would the person sign in with?
Is there a signed processing agreement covering that exact plan?
Is the transfer outside the EEA recorded, with its legal tool named?
Has someone screened it against the DPC's DPIA list and kept the note?
Built from GDPR Articles 28, 35 and 44 to 46 and the Law Society of Ireland's generative AI guidance. General information, not legal advice for your practice.
I wouldn’t let a trainee near a consumer chatbot with an affidavit, however tidy its settings look. A firm that does adopt a business plan should say so in the data paragraph of its engagement letter, because a client may well ask.
The same question now turns up on insurance paperwork, and the AI section of a cyber proposal form is easier to answer once the decision above is written down.
Is an AI tool a data controller or a data processor?
It depends on the account and the purpose, which is why the question keeps coming up. On a business plan the provider normally acts as your processor for the content you send. On a personal account it is a controller in its own right, under consumer terms your firm never signed.
Image editors, transcription apps and browser add-ons follow the same logic: read who the terms say decides the purposes. A privacy layer in the path counts as well; Skyflow, for one, operates its own vault whichever way you deploy it.
| Situation | The provider's role | What you need |
|---|---|---|
| A staff member on a personal chatbot account | Controller, for that person's account | Nothing your firm can enforce: keep client data out |
| The firm's workspace on a business plan | Processor for your content | An Article 28 agreement that names that plan |
| The provider improving its models with your content | Controller for that purpose | A contractual exclusion, not a settings toggle |
| A masking or routing layer in front of the model | Processor or sub-processor | Its own line in your record: Cloudflare's AI Gateway runs on Cloudflare's network, and Protecto sits in the path too |
These are the five questions I would send any supplier, and none of them needs a lawyer in the room. Copy them, send them, and file the replies with the date: several of these documents were revised during 2026.
Five questions for the supplier
Send them as one email and file the replies with the date you got them.
Which named plans does your processing agreement cover? Where is your sub-processor list, and how much notice of changes? Is your US transfer tool Data Privacy Framework certification or standard contractual clauses, and which version? What is the retention period, and what survives deletion? Which roles in your company can read our content, and why?
Processor terms under Article 28 GDPR; US transfers under Chapter V.
GDPR and US transfers: SCCs or the Data Privacy Framework
Most assistants send data to the United States at some point. Article 1 of the EU-US adequacy decision of 10 July 2023 covers only organisations included in the Data Privacy Framework List kept by the US Department of Commerce, so the test is whether your provider’s US company is on that list.
The General Court dismissed Philippe Latombe’s challenge to that decision on 3 September 2025. He appealed to the Court of Justice on 31 October 2025 (Case C-703/25 P), and no ruling had been given by 7 November 2026, so the decision applies while the appeal runs.
A provider that isn’t listed relies on standard contractual clauses instead. OpenAI’s Europe policy and Anthropic’s both cite adequacy decisions and those clauses without mentioning the Framework, as our Claude guide sets out for Anthropic.
The US company is on the DPF List
- Record the certification and its scope on the day you check
- Note that adequacy covers listed organisations, not the country
- Re-check at renewal: entries lapse and recertify
It isn't on the list
- Record the standard contractual clauses and their module
- Keep your own assessment of the destination country's law
- Note retention too: uploaded photos can follow a different clock from text
I don’t trust comparison tables on this point, mine included: entries lapse, and a ruling on that appeal could change the footing. Searching the Department of Commerce list on the day you sign takes two minutes, and a record that just says “cloud” is the first gap a client’s data protection officer spots.
Do you need a DPIA for AI? The DPC’s Article 35(4) list
Article 35 makes an impact assessment mandatory where processing is likely to be high risk. The DPC’s own list adds ten processing types for which a DPIA is mandatory once a documented screening shows likely high risk, and its list of risk factors puts new or novel technologies first.
Tick what applies to the way your firm would use the assistant. The screening note is a record in its own right, so keep it whichever way it comes out; health and legal files hit the last two boxes fastest, which is why the special category rules matter here.
Screening your AI use against the DPC's list
0 of 6 apply
None applies. File the screening note with the date and your reasons: the DPC expects the decision itself to be documented.
At least one listed type applies. If the screening finds likely high risk, the DPIA is mandatory and comes before the first use.
Six of the triggers that fit office AI use, from the DPC's Article 35(4) list and Article 35(3) GDPR. The full list has ten items.
A GP practice is the obvious case, and what comes out of a referral letter first is set out separately. I would do the screening for any practice, ticked boxes or not: it is a page, and it is the page the DPC asks for.
What staff should never paste into an AI chat, whatever the plan
A processing agreement moves accountability. It doesn’t satisfy data minimisation. A question about a clause needs the clause, not the parties, and a summary of a consultant’s report needs the findings, not the name and date of birth above them, which is how Irish healthcare teams should treat every referral.
| What goes in | Why it stays out | Where to read more |
|---|---|---|
| PPS numbers | A State identifier, and the question rarely needs it | Who may use a PPSN |
| Whole files, to answer one point | Everything else in the file is surplus | What to take out |
| PDFs with black boxes drawn on | The text underneath can still be read by a tool | Redacting a PDF properly |
| Diagnoses, union membership, beliefs | Article 9 needs a condition of its own | Special category data and AI |
| Privileged material | The Law Society warns privilege may be lost | For solicitors |
Taking identifiers out lowers what the provider receives. It doesn’t take the text outside the GDPR while you keep the list that puts them back, as the Irish guide to pseudonymised data explains.
My own rule is blunt: if the answer wouldn’t change without the name, the name doesn’t go.
Irish law on top: the Data Protection Act 2018 and the AI Act
The GDPR applies directly; the Data Protection Act 2018 adds the Irish layer, including the powers the DPC used against X. The EU AI Act is a separate regulation about the system and its risk class, and our guide to the AI Act in Ireland covers who enforces it here.
| Section | What it does | Why it matters for AI use |
|---|---|---|
| 11 | Makes the Commission the supervisory authority | A complaint from Ireland about your AI use goes to the DPC |
| 31 | Sets the age for Article 8 consent at 16 | Consumer AI apps used by teenagers |
| 36 | Lists suitable and specific measures: access limits, erasure time limits, training, logging | What DPIA item 10 points back to |
| 47 | Special category data for legal advice and proceedings | A condition for solicitors, not a contract |
| 110 | Inquiries by the Commission | Google's PaLM 2 and both X inquiries |
| 134 | Urgent High Court application to suspend or restrict processing | Used against X in August 2024 |
| 141(4) | Caps fines on most public bodies at €1,000,000 | Orders to stop still apply in full to bodies with a statutory duty |
I wouldn’t read that €1,000,000 cap as comfort for a council: an order to stop processing would hurt a service far more than the fine. The guide for local authorities works through that side.
If your provider sits outside the EU altogether, whether the AI Act applies outside the EU is its own question. None of this is legal advice: whether section 47 or a DPIA applies to your files is for your solicitor or DPO.
Before the first paste: putting it in writing
The DPC’s 2025 annual report counted 16,160 new cases from individuals, up 45%, and its chair said many involved people using AI to make their complaints. The next complaint about your firm may be drafted by a chatbot, and I expect it to ask the questions in this guide.
Six steps, contract before office
The contract side
1. Choose the firm's business plan, never personal accounts 2. Sign and file the processing agreement for that plan 3. Record the transfer tool and the retention periodsThe office side
4. Screen against the DPC's DPIA list and keep the note 5. Write the rule on what may be pasted and check what your cyber cover asks 6. Take names and numbers out before anything is sentFirms with many users can roll this out through Nonimo for organisations or with a partner. Product detail for each assistant is in our other guides.
Step six is the one Nonimo handles. On a Mac or Windows computer it swaps names and numbers for labels before the text leaves, shows you every change first, and keeps the list that restores them on your side. If that is the gap in your office, start with Nonimo in Ireland.
For software that calls a model through an API, the Gateway masks personal data on your own server before each request goes out.
Either way, your text never reaches us, and our security page says how.
Sources
- Data Protection Commission, AI Insights Report, 25 September 2026. About 180 AI engagements, 2021 to 2025; generative engagements by year; the Meta, X and Google matters; “will never approve”. Source
- Data Protection Commission, AI, Large Language Models and Data Protection, 18 July 2024. What a deployer should understand first, and the risk list. Source
- Also from the DPC, cited without links: statement on LinkedIn AI training (7 November 2025); X inquiry (17 February 2026); Google fine (21 September 2026); Annual Report 2025 (30 June 2026); Article 35(4) DPIA list.
- Regulation (EU) 2016/679 (GDPR), cited without a link. Articles 9, 12, 28, 35 and 44 to 46.
- Data Protection Act 2018. Sections 11, 31, 36, 47, 110, 134 and 141(4). Source
- Commission Implementing Decision (EU) 2023/1795. Article 1 limits adequacy to the Data Privacy Framework List. Source
- Court of Justice, Latombe v Commission, C-703/25 P, appeal lodged 31 October 2025. Appeal against the General Court judgment of 3 September 2025 (T-553/23) dismissing the action; pending. Source
- Law Society of Ireland, generative AI guidance. Consumer versions unsuitable; enterprise tools no guarantee; privilege. Source
- OpenAI, Europe privacy policy, updated 24 August 2026. OpenAI Ireland Limited as controller; the DPC as lead supervisory authority; adequacy and SCCs. Source
- Anthropic, Privacy Policy, effective 10 September 2026. Anthropic Ireland, Limited; transfer tools; training opt-out. Source
- Google, Gemini Apps Privacy Hub. Google Ireland Limited as provider in the EEA. Source
- OpenAI, Enterprise privacy, updated 8 January 2026. Processing addendum for ChatGPT Business, Enterprise and the API; no training on business data by default. Source
- Microsoft Learn, Data, Privacy and Security for Microsoft Copilot. No foundation model training; Anthropic models outside the EU Data Boundary. Source
- Microsoft Learn, Claude models from Anthropic in Microsoft Online Services. Off by default for EU, EFTA and UK tenants. Source
Checked on 8 November 2026.
Common questions
What AI tools are GDPR compliant?
None is compliant by itself. The GDPR judges what your organisation does with personal data, so the same assistant can be lawful in one office and unlawful in the next.
Is AI GDPR compliant?
The GDPR doesn't ban AI. It applies the moment personal data goes in, so you need a lawful basis, a processor contract, a transfer tool and, where the risk is high, a DPIA.
How do you protect personal data from AI?
Send less of it. Use a business plan with a processing agreement, set retention, and take names and identifiers out of the text before it reaches the model.
Is ChatGPT GDPR compliant?
Not by itself, and the DPC won't certify any chatbot. OpenAI signs a processing addendum for ChatGPT Business, Enterprise and the API; a personal account has none, so client data stays off it.
Is it safe to put confidential information into Microsoft Copilot?
Only on a work account, and even then send the minimum. Under your Microsoft 365 contract, prompts and Graph data don't train foundation models, and Claude models stay off for EU tenants unless an admin opts in.
Can Irish solicitors use AI with client data?
Yes, but not on consumer accounts. The Law Society of Ireland says free and paid consumer versions are unsuitable for client data, and enterprise tools still need due diligence.
Is an AI image editing tool a data controller or a data processor?
It depends on the account and the terms. Under a business contract acting on your instructions it is usually your processor; under consumer terms it decides its own purposes and is a controller.
Is Claude GDPR compliant?
Claude is no more compliant on its own than any rival. Anthropic Ireland, Limited is its European controller, and consumer chats train models unless you opt out, so business terms matter for work.