Which AI tools are UK GDPR compliant? How to use them at work
· Updated

Joaquín Trapero in AI and privacy specialist, and founder of Nonimo.
Plenty of AI vendors call their product “GDPR compliant”, usually meaning the EU text. The UK GDPR has been a separate law since the end of 2020, and its transfer rules were rewritten on 5 February 2026. Either way, the duties sit with the organisation deciding why personal data goes in, not with the tool.
So this page doesn’t rank tools. It lists what a UK employer has to check, then compares the business tiers of ChatGPT, Claude, Gemini and Copilot on those points, using each company’s own documentation. If something has already been pasted, read whether that paste is a data breach first.
No AI tool is UK GDPR compliant on its own; your use of it can be. A business tier brings a processor contract and, usually, no training on your data. You still need a lawful basis, a UK transfer route, a DPIA where the ICO's list catches you, and a written staff rule.
Is AI GDPR compliant? The answer depends on who decides
Article 28 of the UK GDPR says what a processor must sign up to: act only on your documented instructions, bind its people to confidentiality, secure the data, help with rights requests, and delete or return everything at the end. A vendor can promise all of that in writing.
What it cannot do is choose your lawful basis or control what your staff type. Those decisions are often made late, after people have started using tools on their own. A sales page that says “GDPR compliant” without linking its processing terms goes straight to the bottom of my list.
Two halves of the same job
The vendor can sign the left column. Nobody signs the right one for you.
What a vendor can put in a contract
Acts only on your written instructionsStaff bound to confidentialityArticle 32 securitySubprocessors only with your authorisationDeletion or return at the endWhat only your organisation can do
Pick a lawful basis, and an Article 9 condition for sensitive dataChoose a transfer route under UK rulesDecide whether a DPIA is neededTell staff what never goes inLeft column: UK GDPR Article 28(3)(a) to (h) and 28(9). Professional rules add their own layer, as with AI in accountancy practices.
UK GDPR and AI at work: six checks your organisation owns
These six come from the UK GDPR, and they are identical whether the assistant was built in California or Cambridge. Run them for one job at a time, such as drafting replies to complaints. HR tasks are the hardest, because special category data sits in ordinary staff files.
Minimising is the cheapest one to pass. If the job runs on a spreadsheet, drop the columns it never reads before upload. Health, ethnicity or union details need an Article 9 condition on top of the Article 6 basis, and special category data carries further rules in the 2018 Act.
The staff rule deserves to be written first. The other five fall apart the day someone opens a personal login, and claim notes describing injuries show how quickly sensitive text reaches a chat window, as in AI at an insurance broker.
Which of the six can you show on paper today?
Tick only what exists in writing for one specific AI task.
0 of 6 in writing
Most of the work is still ahead. Keep personal data out of the tool until the contract and the staff rule exist.
Close. The gaps left are usually transfers and the DPIA, both covered further down.
All six on paper. Diarise a review for when the vendor changes its terms or your task changes.
Our checklist, built from UK GDPR Articles 5, 6, 9, 28, 35 and 44A. For the staff rule, adapt our AI policy template.
Does ChatGPT comply with GDPR? Which tier you have, and what’s missing
The login decides more than the brand. A personal account, free or paid, is a contract between the provider and the person typing; your firm isn’t a party to it, so it can’t instruct, audit or demand deletion. A work account run by your administrators is where processor terms begin.
Deleting a chat later doesn’t repair a paste made on the wrong account, because the provider removes deleted history on its own timetable.
Of everything the four vendors publish, Microsoft’s line for customers outside the EU is the one every UK buyer should read twice: queries may be processed in the US, the EU or other regions. Use the decision below to see what your tier gives you and what stays open.
Which tier do you have, and what's still missing?
Answer for the account staff really use, not the one on the invoice.
How does the person sign in?
Which assistant?
From each vendor's own documentation, read on 8 November 2026 (see Sources). A summary, not the contract: the terms attached to your plan win.
International transfers under UK rules: adequacy, the IDTA, the UK Addendum and the data bridge
Since 5 February 2026, transfers sit in Articles 44A to 49 of the UK GDPR. Data can leave under regulations approving the transfer (the old adequacy route), Article 46 safeguards or an Article 49 derogation. Transfers to EEA states are treated as approved, under Schedule 21 to the 2018 Act.
For the US, the UK-US data bridge has applied since 12 October 2023, but only to companies certified under the UK Extension to the Data Privacy Framework. For anyone else, the usual safeguard is the UK’s standard clauses (the IDTA, or the UK Addendum to the EU clauses), plus Article 46’s data protection test.
That test is met if protection after the transfer would be “not materially lower” than under UK law. Write that judgement down, one dated page per vendor. A proxy that sees the prompt joins the chain too, unless you run it inside your own network. None of this replaces a solicitor reading your actual contract.
Where the data goes, and the UK route that covers it
The highlighted row is the common case with US assistants.
| Where it goes | UK route | What to keep on file |
|---|---|---|
| Stays in the UK | Not a transfer to a third country | The vendor's statement on processing location |
| An EEA company, such as a Dublin subsidiary | Treated as approved (Schedule 21, paragraphs 4 and 5, DPA 2018) | Its own onward transfer terms |
| A US company certified under the UK Extension | UK-US data bridge (Article 45A regulations) | A dated record of its status on the list |
| A US company not certified for the UK | IDTA or UK Addendum (Article 46(2)(d)) | Signed clauses and your data protection test note |
| Anywhere, in a specific situation | Article 49 derogation | Which Article 49 condition you rely on, and why |
UK GDPR Articles 44A, 46 and 49 as amended from 5 February 2026; DSIT's data bridge explainer. To send less abroad in the first place, weigh a private model against a privacy proxy.
Do you need a DPIA for AI? Where the ICO’s list catches you
The ICO’s list of processing that always needs a data protection impact assessment opens with innovative technology, and names AI. That alone doesn’t trigger one. The DPIA becomes required when the AI use also meets any single criterion from the European guidelines, and the assessment comes before the processing starts.
Two criteria catch employers. Employees count as vulnerable because of the power imbalance, so AI on HR files qualifies; so do patients receiving care, which makes AI in a GP practice a DPIA question from day one. One professional’s client files are not “large scale”, the ICO says; a hospital’s are.
When the answer is borderline, write the DPIA. The ICO’s own advice is to do one if in any doubt, and a short assessment costs far less than arguing afterwards that none was needed.
AI plus one of these means a DPIA
Your AI use already counts as innovative technology. Tick anything else that's true of the task.
Nothing ticked: the ICO's list doesn't make a DPIA mandatory here, though the ICO recommends one if you're unsure.
With AI, that's enough for the ICO's list: do the DPIA before the processing starts.
The ICO's page "When do we need to do a DPIA?" (under review after the Data (Use and Access) Act) and the European criteria it refers to, in our wording. For NHS settings, see whether NHS staff can use ChatGPT.
Is it safe to put confidential information into Microsoft Copilot?
On a work account, Microsoft says prompts get the same contractual protection as your mail in Exchange and files in SharePoint, and Copilot has opted out of the human abuse monitoring offered in Azure OpenAI. The weak spot is inside your tenant: Copilot shows anything a user can already open, so loose permissions become answers.
Web search is the second gap. When Copilot grounds an answer on the web, it sends a short query to Bing with user and tenant identifiers removed, and Microsoft handles it as an independent controller outside the Data Protection Addendum. Where privileged files are involved, I want web grounding off for those users.
Files also carry more than their visible text. Before a document lands on a site Copilot can search, clear the comments and tracked changes in Word that nobody meant to share.
Microsoft 365 Copilot: inside the DPA, and outside it
The right column is where UK firms get caught.
Covered by Microsoft's terms
Prompts and responses, with Microsoft as processorNo training of foundation models on themStored Copilot history, including Teams meeting chatsYour retention policies and audit applyOutside it, or your job
Web queries to Bing: Microsoft as independent controllerPermissions: Copilot surfaces what users can openSensitivity labels and Purview retention set upAnthropic or OpenAI models in Copilot: extra terms may applyMicrosoft Learn, "Enterprise data protection" and "Data, Privacy, and Security for Microsoft Copilot", both read 8 November 2026. Once you've chosen a provider, name it in your engagement letter.
Are there any AI regulations in the UK? What applies on 8 November 2026
There is no UK AI Act. In February 2024 the government said it would not rush to legislate and left AI to existing regulators, while sketching possible binding rules for developers of the most advanced models. For personal data, that leaves the UK GDPR and the 2018 Act, both amended by the 2025 Act.
The regulator changed shape on 30 September 2026, when the Information Commission replaced the Information Commissioner, though its website still says ICO. Its guidance on AI and data protection dates from 15 March 2023 and is under review. And the EU AI Act can reach a UK business selling into the EU.
Is there a British AI tool? The government built Humphrey, a bundle of AI tools for civil servants; its consultation tool was first used on a live consultation by the Scottish Government. I wouldn’t choose a supplier for its flag: a British assistant on US servers raises the same transfer question as an American one.
The rules that touch an AI rollout in the UK
Status on 8 November 2026.
| Rule or body | Status | What it means for you |
|---|---|---|
| UK GDPR and Data Protection Act 2018 | In force, amended by the Data (Use and Access) Act 2025 | Every check on this page |
| Transfer rules (Articles 44A to 49) | Rewritten from 5 February 2026 | The data protection test for Article 46 safeguards |
| Information Commission | Replaced the Information Commissioner on 30 September 2026 | Same website and guidance, new name |
| ICO guidance on AI and data protection | Last updated 15 March 2023, under review | Still the regulator's main text on AI |
| A UK AI Act | None | Sector regulators apply their own rules |
| Your cyber insurer | Not a law, but asks about AI at renewal | The AI questions on a cyber questionnaire |
Data (Use and Access) Act 2025, sections 117 to 119, in force 30 September 2026 by S.I. 2026/1015; the government's AI regulation response of 6 February 2024. Public bodies have extra duties: see AI in local government.
Cover for a data incident caused by an AI tool is a separate buying decision, set out in our UK cyber insurance comparison.
Making your GDPR compliant AI use hold up: take the client out of the prompt
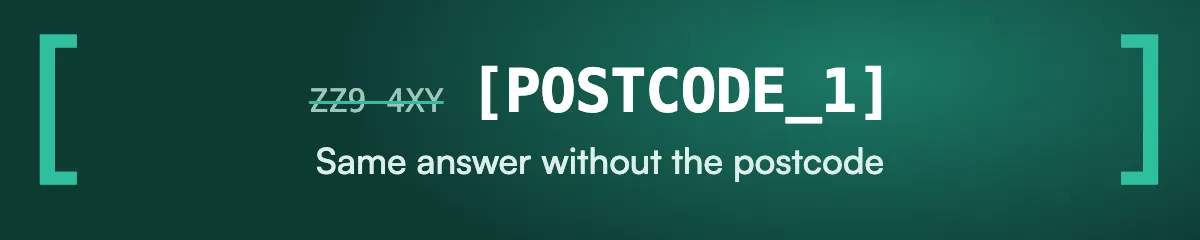
If I had one control to pick, it would be minimisation: Article 5(1)(c) wants only what the task needs. A prompt without the client’s name, NI number or postcode usually gets the same answer. It isn’t anonymous afterwards, since replaced identifiers leave pseudonymised data, but far less can leak.
Nonimo for UK teams does that step on your own computer: it swaps the client’s identifiers in the prompt for labels before the assistant sees them and puts them back in the reply, so your AI use has much less personal data to account for.
Your text never reaches us, as our security page explains, and you can undo any replacement before sending.
An invented prompt, before and after
The question survives. The driver doesn't.
Draft a reply to Gareth Pennock, ZZ9 4XY, NI QQ 98 76 54 B, about his disputed overtime at Whitlow Haulage Ltd in October.
Draft a reply to [PERSON_1], [POSTCODE_1], NI [NI_1], about his disputed overtime at [COMPANY_1] in October.
Made-up person and company. ZZ is not a real postcode area and QQ is a prefix HMRC never issues. More on taking NI numbers out before AI.
Choosing between redaction tools is its own question, covered in our guide to PII redaction software.
One person or a small office
- Install on each computer that uses AI
- Plans for UK users
A whole organisation
- Roll out with your data protection lead
- Deployment for organisations
You advise other firms
- IT providers and consultants
- The partners programme
For developers whose software calls a model directly, Cloudflare’s gateway can block a prompt that matches a personal data profile.
Tools and sectors not covered here are in our guides index.
Sources
- UK GDPR, Article 28, legislation.gov.uk. The processor contract terms, in writing.
- UK GDPR, Article 46, legislation.gov.uk. Safeguards and the data protection test, as amended from 5 February 2026.
- ICO, Guidance on AI and data protection. Updated 15 March 2023, under review after the Data (Use and Access) Act.
- ICO, When do we need to do a DPIA?. Innovative technology including AI, the European criteria, employees and patients as vulnerable.
- DSIT, UK-US data bridge: explainer. Transfers to certified US organisations from 12 October 2023.
- DSIT, Government-built “Humphrey” AI tool reviews responses to consultation for first time, 14 May 2025. Humphrey and its Consult tool.
- Data Privacy Framework list, US Department of Commerce. The list the UK-US data bridge regulations rely on.
- Microsoft Learn, Enterprise data protection in Microsoft Copilot. DPA and Product Terms, Microsoft as processor, Bing queries outside them.
- Microsoft Learn, Data, Privacy, and Security for Microsoft Copilot. Permissions, processing regions outside the EU, abuse monitoring opt-out.
- OpenAI, Data controls in the OpenAI platform. No training by default, 30-day logs, UK storage only.
- Anthropic, Commercial Terms of Service. No training on customer content, DPA incorporated, Anthropic Ireland for UK customers.
- Anthropic, Privacy Policy. Customer content processed under customer agreements; UK transfer mechanisms.
- Google, Generative AI in Google Workspace Privacy Hub. Cloud Data Processing Addendum, training and human review.
- Google, Gemini Apps Privacy Hub. Human reviewers on consumer accounts; different terms for work accounts.
Accessed 8 November 2026.
Common questions
Is AI GDPR compliant?
No tool is UK GDPR compliant on its own. The duties fall on your organisation: a lawful basis, an Article 28 contract with the vendor, a transfer route under Article 44A and a rule on what staff type.
Does ChatGPT comply with GDPR?
It can be used lawfully, but not through a personal account. A firm needs a business tier with processor terms, a UK transfer route and a rule on what staff may enter.
Is Copilot GDPR proof?
On a work account, Microsoft acts as your processor. Its Data Protection Addendum and Product Terms cover prompts and responses, and they aren't used to train foundation models. Your own duties still apply.
Is it safe to put confidential information into Microsoft Copilot?
Safer on a work account, with one catch. Copilot shows anything the user is allowed to open, so loose SharePoint permissions turn into answers. Tidy access before rollout.
Is Microsoft Teams GDPR compliant in the UK?
Teams can be used lawfully; the duties stay with your organisation. Microsoft says Copilot chats in Teams meetings are stored under the same commitments as your other Microsoft 365 content.
Is there a British AI tool?
The government built one, Humphrey, for civil servants. Councils have trialled part of it too. Under the UK GDPR a supplier's nationality settles nothing: where the data is processed, and under which contract, does.
Are there any AI regulations in the UK?
There is no UK AI Act. AI that touches personal data falls under the UK GDPR and the Data Protection Act 2018, as amended in 2025, plus sector rules.
Should you put personal data into AI?
Only when the task truly needs it. Data minimisation is a UK GDPR principle, and most drafting or summarising works just as well with names and numbers replaced.