Which AI tools can you use under Australia's Privacy Act?
· Updated

Joaquín Trapero in AI and privacy expert, and founder of Nonimo.
No AI tool is approved under the Privacy Act 1988. There’s no register and no certificate. The Act looks at what your organisation does with personal information, so the same assistant can be fine in one office and a problem in the next.
This guide is for picking a tool before anything goes in. If a paste has already happened, start with whether it counts as a reportable breach instead.
Any AI tool can be used lawfully, and none is lawful by default. Judge each tool by its plan: training on your input, retention, overseas access (APP 8) and deletion (APP 11). Business products from OpenAI, Anthropic, Microsoft and Google don't train on your content by default. Personal accounts differ.
Does the Privacy Act apply to AI at your business?
The OAIC’s guidance on commercially available AI products, published 21 October 2024, is plain: the Act applies to every use of AI involving personal information. The catch is “APP entity”. Most businesses with annual turnover of $3,000,000 or less sit outside it, under section 6D.
Section 6D(4) pulls some of them back in: health service providers holding health information, businesses trading in personal information, Commonwealth contractors and credit reporting bodies. The full tick-list sits in our guide to sensitive information, so I won’t repeat it here.
Being exempt describes your business, not the file. A health client’s records don’t get safer because your turnover is small, and a privacy complaint isn’t the only way a leak hurts you.
Is the Privacy Act watching your AI use?
Pick the description closest to you.
Covered. One year over the $3,000,000 line, counted from when the business began, is enough to make you an APP entity. Every principle then applies to what staff paste.
Covered, at any size. A provider of a health service holding health information outside employee records isn't a small business operator, s 6D(4)(b). Clinics also have Ahpra's expectations about AI and patient data.
Covered for AML/CTF work. Since 1 July 2026, lawyers, conveyancers, accountants and real estate professionals providing designated services are reporting entities. The OAIC says small ones must comply with the Act for those activities. Identity checks are the obvious overlap, which is where our page for property managers and agents starts. A licence copy watermarked for one matter or a passport copy marked the same way limits reuse. Tax agents also have the TPB's expectations.
Not this Act. Councils answer to state privacy law. AI in Australian councils covers each state.
Probably exempt. You can still opt in, and a client contract may require you to handle their data as if you were covered. Payroll with tax file numbers brings its own rules, set out in redacting a TFN before AI.
Privacy Act 1988, s 6D(4) and s 6E(1A); OAIC guidance for AML/CTF reporting entities (updated 28 August 2026). A guide to who is covered, not a ruling on your business.
The AML/CTF limb catches people out. A Victorian licence copy collected for a client check now sits under the APPs, even in a three-person practice, and it is exactly the file that ends up pasted into a chatbot.
Privacy focused AI tools and the word “compliant”
Search for privacy focused AI tools and you’ll find plenty of products calling themselves Privacy Act compliant. A product can’t be. The APPs bind entities, and a vendor can only hand you commitments that make your own compliance easier to show.
This one annoys me: a badge on a pricing page says nothing about what your staff paste. Two firms on the same plan can be in opposite positions if one has a written rule on what may be entered and the other doesn’t.
Wording on a vendor's page, read against the APPs
What each line can tell you, and what it leaves with your organisation.
| The page says | What it can tell you | Still yours to settle |
|---|---|---|
| "Privacy Act compliant" | Nothing on its own: the APPs bind your organisation, not a product | Every principle, starting with what staff may enter |
| "We don't train on your data" | One setting, on one plan | Whether it's in the contract, and which account staff sign into |
| "Data stays in Australia" | Where it's stored at rest | Where the model reads it, and who can reach it (APP 8) |
| "ISO 27001 certified" | An auditor looked at its security management | Training, retention and overseas access, which the certificate doesn't cover |
| "Delete your chats any time" | The copy you can see | Logs, feedback and reviewed chats kept longer (APP 11) |
| Nothing about clients | Correct: it can't speak for you | Whether clients were told (APP 5) and the purpose fits (APP 6) |
My reading of APPs 5, 6, 8 and 11 against the kind of wording vendors use; the quoted lines are generic, not taken from one vendor. Whether the EU AI Act also reaches you is a separate check.
The right-hand column costs nothing but time, and it’s where I’d spend the first afternoon. For a firm of any size, our page for organisations shows where the written rule meets the desk.
Private AI platforms compared: training, retention, location
Below is what four vendors’ own documentation says about six common plans. No marketing pages and no third-party summaries. I don’t rank them: the table exists so you can match a plan to your data, and these settings change often.
Six AI plans, from the vendors' own documents
| Plan | Trains on your input? | Retention | Where it sits |
|---|---|---|---|
| Gemini app, personal Google account | Yes, while Keep Activity is on; a subset of chats is read by human reviewers | Auto-delete at 18 months by default; reviewed chats up to 3 years | Not stated in the privacy hub |
| Claude Free, Pro, Max | Only if you allow it, or a chat is flagged for safety review | Feedback kept up to 5 years | Not covered in the pages read |
| Claude Team, Enterprise and API | No by default; a thumbs-up or thumbs-down stores the whole conversation | Feedback up to 5 years; admins can switch rating off | Stored in the US; traffic may be routed to the US, Europe, Asia and Australia |
| OpenAI API | No, unless you opt in | Abuse monitoring logs up to 30 days; zero retention by approval | Australian storage at rest available; processing not in Australia |
| Microsoft 365 Copilot | No: prompts, responses and Graph data aren't used for foundation models | Set by your admins in Purview; users can delete history | Australian storage with the Advanced Data Residency add-on; queries may be processed in the US, EU or elsewhere |
| Gemini in Workspace | No, without your permission; not human reviewed | Gemini app: 3, 18 or 36 months, set by admins (18 by default); side panel in Gmail and Docs: 90 days to indefinite | No Australian region named in the hub |
Vendor pages read 8 November 2026: Google privacy hubs (October 2026), Anthropic privacy centre (consumer 16 March 2026, commercial 18 August 2026, servers 15 June 2026), OpenAI API data controls, Microsoft Learn (Copilot privacy, Advanced Data Residency). Work plans highlighted.
ChatGPT’s plans, with dates, are in what ChatGPT does with your data. On every row the plan matters more than the brand, and settings live per account. Turning training off on the office account does nothing for staff signed in with their own.
The table also can’t tell you what goes in the box. Often it’s a whole export, and a client list saved as CSV carries every column with it.
A plan table is no help when staff use five tools. Watching what leaves across all of them is a different product category, employee-wide DLP such as Nightfall, bought for the whole network rather than per plan.
Can Australian data be stored overseas? APP 8 in practice
Yes. The Act has no data localisation rule for businesses. APP 8.1 asks for reasonable steps, before you disclose personal information overseas, so the recipient doesn’t breach the APPs. Where APP 8.1 applied to the disclosure, section 16C then treats that recipient’s breach as yours.
The word doing the work is “disclose”. Chapter 8 of the APP Guidelines (version 1.3) says data routed through an overseas server in transit is usually used, not disclosed, and offshore storage can be too if a binding contract keeps you in control.
Storage in Australia is the detail I’d weigh least. A model still has to read the prompt to answer it, and the table above shows where that happens. Anthropic, for one, says safety review and support can happen wherever it or its affiliates operate.
Where the prompt goes, and what APP 8 makes of it
| What happens to the text | OAIC reading | What it means for you |
|---|---|---|
| Passes through an overseas server on its way | Usually a use (8.10) | The routing alone doesn't trigger APP 8 |
| Stored offshore, contract limits the provider to storage, you can retrieve and delete | May be a use (8.14) | Works for storage; the contract has to give you effective control |
| The overseas provider can access or change it: model processing, safety review, support | No longer mere transit once the recipient can access or modify it (8.10) | APP 8.1 reasonable steps, and s 16C accountability |
| Stored at rest in Australia, processed offshore | Not addressed directly | My reading: the processing leg still reaches an overseas recipient |
| Your own app calls a model API through a proxy, such as Cloudflare's AI Gateway | Two recipients, not one | Each gets the prompt unless identifiers are masked on your own server first |
OAIC APP Guidelines chapter 8, paragraphs 8.10 and 8.14; Privacy Act s 16C. Counting model processing as access in the third row is my reading, as are the last two rows; the OAIC hasn't said either.
APP 8.2 offers ways around 8.1, among them a substantially similar overseas law, express consent after a specific warning, or a country prescribed by regulation under APP 8.3. Chapter 8 names no prescribed country, so for a US vendor the contract is the realistic route.
Questions for an AI data privacy vendor, from APP 8
The OAIC generally expects an enforceable contract requiring the overseas recipient to handle the information under the APPs, other than APP 1. Paragraph 8.16 lists what that contract should cover, and the AI guidance adds questions about training and third parties.
If a vendor won’t answer the breach question in writing, that’s my answer too. Hand the list to whoever runs your systems and keep their replies on file.
What to ask before client data goes into an AI tool
Tick each one the vendor has answered in writing.
Answered: 0 of 9
Too many gaps to call this reasonable steps. Keep personal information out until they're filled.
Close. Chase the missing answers before the first client file goes in.
Everything answered. File the replies with your assessment of the tool.
Questions drawn from OAIC APP Guidelines chapter 8, paragraph 8.16, and the OAIC's guidance on commercially available AI products. The thresholds are my own rule of thumb.
Australian law doesn’t use the term data processing agreement. A GDPR addendum binds a vendor to European principles, which isn’t the same as binding it to the APPs, so read what yours actually promises.
APP 11 and how long an AI tool keeps your prompts
APP 11.1 asks for reasonable steps to protect personal information you hold. APP 11.2 asks you to destroy or de-identify it once you no longer need it for a permitted purpose. A prompt kept in the history of an account you control is, on my reading, a copy both reach.
The OAIC’s AI guidance warns that information entered into generative AI may be potentially impossible to remove. So the retention column matters as much as the training one, and clearing a ChatGPT history means memories, files and shared links too.
Five years for a thumbs-up surprised me more than anything else I read for this page. One click on a rating button keeps the whole conversation.
How long a prompt can outlive the chat
Fixed periods named in each vendor's own documents.
Bars scaled to 60 months, the longest fixed period named; Google's app settings also offer "indefinite", which no bar can show. Google Gemini Apps and Workspace privacy hubs; OpenAI API data controls; Anthropic privacy centre, all read 8 November 2026. Microsoft leaves Copilot retention to your own Purview policy, so it has no bar.
Whether text with the names swapped out still counts as personal information turns on who holds the key.
Deleting is also harder than it looks inside the file itself. A TFN left as hidden text in a Word file is still in the record you uploaded.
AI for confidential files: does this tool fit this data?
The vendor table tells you what a plan does. The question an office actually faces is narrower: this file, this tool, today. Run it through APP 8, APP 11 and the sensitive information rules in that order.
Skip the brand debate when the prompt works with nobody in it. Most of the work below disappears once the identifiers an Australian file tends to hold are gone.
Does this tool fit this data?
Which account would the text go into?
Does the vendor's contract bind it, and its subprocessors, to the APPs, with breach notice to you?
Can you set retention and delete what goes in?
Does the text hold sensitive information: health, union, criminal record, beliefs?
Would the answer be just as good with names and numbers swapped for labels?
The order and wording are mine. Each step rests on the Privacy Act (APP 6, APP 8, APP 11, s 16C) or the OAIC's guidance on commercially available AI products.
The OAIC’s own example is an insurer’s staff entering customer details into a chatbot: a disclosure to the chatbot’s owner, it says. A broker working from a claim file is in that position, and our page for insurance brokers covers what to strip first.
Recording your AI tool choice under the Privacy Act
A setting changed in March leaves no trace by September. What exists on the day a client, an insurer or the OAIC asks is what you wrote down. Start the policy from an AI policy template and keep one register line per tool.
I’d write the register entry before the first paid seat, because its questions are the ones that change the purchase. Much of it is also what a broker asks before quoting an Australian cyber policy.
A register line for each AI tool
Copy it, then fill one per tool and plan.
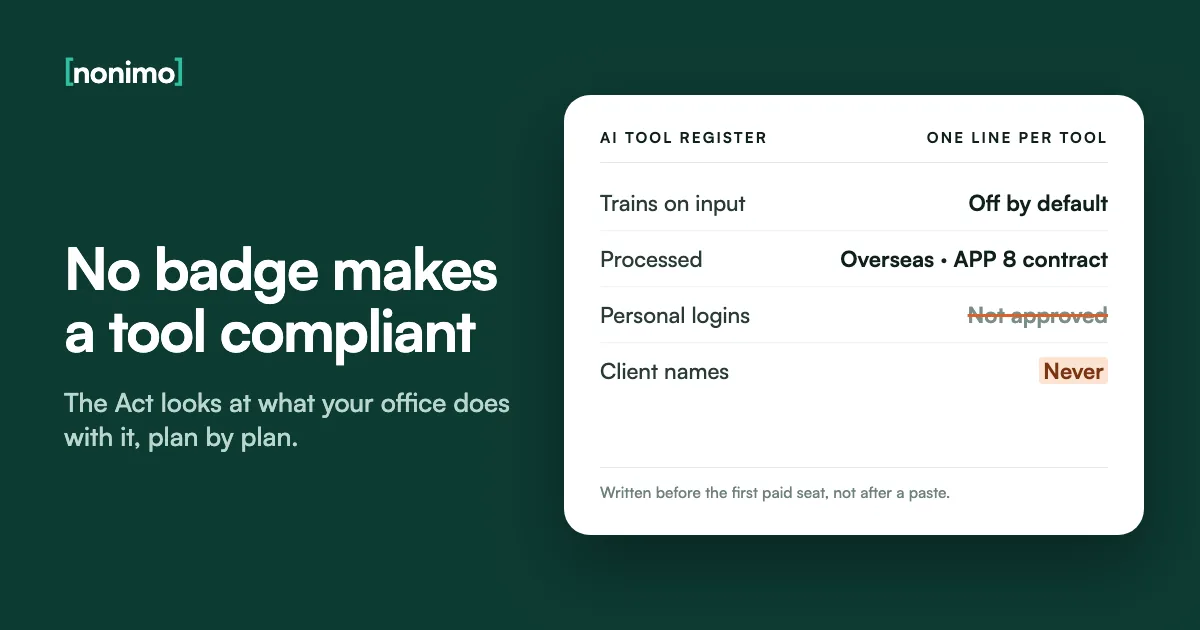
Tool and plan: ___. Who may use it, on which accounts: ___. Data allowed in: ___. Data never allowed in: sensitive information, TFNs, ___. Training on our content: off by contract / by setting / unknown. Stored in: ___. Processed in: ___. Retention set to: ___. Contract binds vendor to the APPs (APP 8): yes / no. Clients told in: privacy policy / engagement letter. Reviewed on: ___ by ___.
My own template, built on APPs 5, 8 and 11. To compare more assistants, our guide library has one page each; for apps built on a model API, see PII redaction software for LLM apps.
A register line reading “client names: never” holds only if something enforces it at the desk. Nonimo for Mac and Windows does that on the computer: names and ID numbers become labels before the prompt reaches the approved tool, and the reply comes back with the details restored.
Your text never reaches us, and the security page explains how.
The plans include a free one with a monthly word limit. This page reads the APPs against vendor documents as they stood in November 2026, and the contract you sign outranks both.
Sources
- OAIC, Guidance on privacy and the use of commercially available AI products, 21 October 2024, updated 17 January 2025. The Act applies to all AI uses with personal information; best practice advice; the insurer example; due diligence; removal from AI systems.
- OAIC, APP Guidelines chapter 8, version 1.3, 3 October 2025. Paragraphs 8.10, 8.14, 8.16, 8.28 and 8.60 to 8.63.
- Privacy Act 1988 (Cth), compilation No. 104, 4 June 2026. Sections 6D and 16C; APP 8.1 to 8.3; APP 11.1 and 11.2.
- OpenAI, Data controls in the OpenAI platform. No training by default, 30-day abuse logs, Australian storage without Australian processing.
- Anthropic, Is my data used for model training? (commercial), updated 18 August 2026. No training by default; feedback stores the conversation for up to 5 years.
- Anthropic, Where are your servers located?, updated 15 June 2026. US storage and routing countries.
- Microsoft Learn, Data, Privacy, and Security for Microsoft Copilot. No foundation model training; Purview retention; processing regions.
- Microsoft Learn, Advanced Data Residency overview. Australia as a local region geography; Copilot covered; add-on licence.
- Google, Gemini Apps Privacy Hub, updated 26 October 2026. Human review, Keep Activity, 18 months, 3 years, 72 hours.
- Google Workspace, Generative AI in Google Workspace Privacy Hub. No training without permission; retention set by admins.
Accessed 8 November 2026.
Common questions
Does the Privacy Act apply to AI?
Yes, whenever an APP entity uses AI with personal information. The OAIC's 2024 guidance says the Act covers all such uses. Most businesses with turnover of $3 million or less are exempt, unless an exception catches them.
Is ChatGPT privacy compliant?
No AI product is compliant on its own. The Privacy Act regulates what your organisation does with personal information, so one ChatGPT plan can be a sound choice in one office and a breach in another.
What is APP 8?
APP 8 governs sending personal information to someone overseas. Before it happens, you take reasonable steps so the recipient doesn't breach the APPs. Under section 16C, you can answer for what that recipient does.
Can Australian data be stored overseas?
Yes, the Privacy Act doesn't ban offshore storage. APP 8 governs disclosure, and the OAIC says storage-only cloud arrangements, under a binding contract that leaves you in control, may count as a use instead.
Are there AI data centres in Australia?
Some AI vendors now store data in Australia. OpenAI's API offers Australian storage without Australian processing, and Microsoft's Advanced Data Residency add-on covers Copilot. Processing can still happen elsewhere.
What are the Australian Privacy Principles?
They're 13 principles in Schedule 1 of the Privacy Act 1988. They set how APP entities collect, use, disclose, secure and correct personal information. For choosing an AI tool, APPs 6, 8 and 11 do most of the work.